Key takeaways
- API integrations expand your attack surface, making credentials, permissions, endpoints, data flows, and third-party connections potential security risks.
- Strong authentication and least-privilege authorization are essential for controlling who can access an API and what they can do.
- Secure API keys, encrypted data, validated requests, and rate limiting help prevent some of the most common API security vulnerabilities.
- Third-party APIs require security reviews, response validation, and failure testing because their risks can directly affect connected systems.
- A pre-launch API security checklist helps teams identify critical gaps across authentication, secrets, data protection, endpoints, and third-party integrations before shipping.
A single user action can trigger a chain of communication across payment platforms, CRMs, cloud services, and other applications. APIs make these invisible connections possible.
But every connection creates another potential point of failure. A leaked credential, excessive permissions, or a vulnerable third-party API can quickly become a security gap, making API security best practices essential from the start.
However, that is why API integration security should be considered before an integration goes live, not after something goes wrong.
Looking to build a secure and reliable web application? Explore top website development companies on Goodfirms and find the right development partner for your project.
This guide covers the essential practices businesses and development teams should follow before shipping an API integration.
API security and API integration security are closely related but not identical. API security focuses on protecting an API, its endpoints, authentication, authorization, and data. API integration security takes a broader view, securing the connections between applications, including credentials, data flows, permissions, third-party APIs, and how integrated systems handle failures.
What Makes API Integrations a Security Risk Before They Go Live?
API integrations create security risks because every connection between applications introduces new credentials, permissions, data flows, endpoints, and third-party dependencies that can potentially be exploited. Before an integration goes live, businesses need to secure the entire communication flow, not just individual APIs, by reviewing how systems authenticate requests, control access, handle data, store credentials, and interact with external services.
The biggest API integration security risks typically include:
- An expanded attack surface: Every API, endpoint, and connected application creates another potential entry point for attackers.
- Exposed credentials: Poorly stored API keys, tokens, or secrets can provide unauthorized access to connected systems.
- Excessive permissions: Over-permissioned integrations can expose more data or functionality than necessary.
- Third-party API risks: External services introduce security dependencies that businesses cannot fully control.
- Sensitive data exposure: Poorly secured requests, responses, or logs can unintentionally reveal confidential information.
- Forgotten or undocumented APIs: Outdated endpoints and unmanaged integrations can remain vulnerable without active monitoring.
This is why a secure API integration should be reviewed as a complete system rather than a collection of individual connections. Businesses planning a new connection can also understand the broader API integration process before evaluating the security controls required to protect it.
Richard Bird, a cybersecurity leader and former Chief Security Officer at Traceable AI, has highlighted a fundamental challenge behind API security: organizations often lack visibility into the APIs operating across their environments.
No time in security history has the answer, “I don’t know anything,” been safe, right? Or secure.
What Are the Most Important API Integration Security Best Practices?
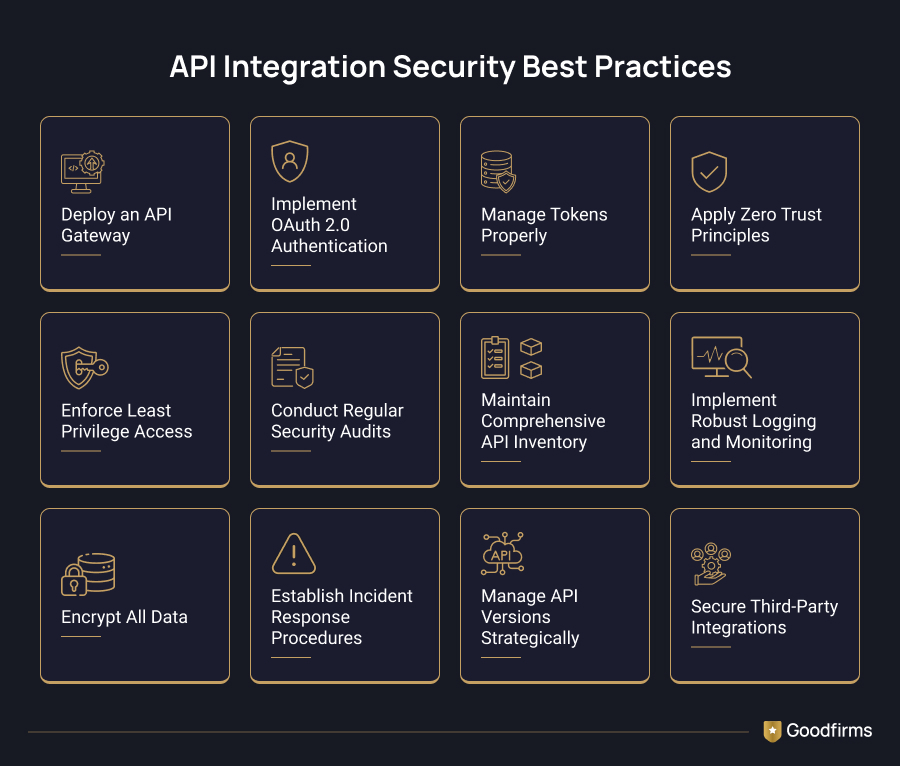
The most important API security best practices are securing authentication, enforcing authorization, protecting API keys and secrets, encrypting sensitive data, validating requests, assessing third-party APIs, and testing integrations before deployment. Together, these controls help businesses reduce unauthorized access, data exposure, and vulnerabilities across connected systems.
Use Strong Authentication
Verify every user, application, or service requesting API access through an authentication method appropriate for the integration. API keys, OAuth 2.0, access tokens, and other methods should be selected based on the system, data sensitivity, and required access.
Enforce Least-Privilege Authorization
Authentication confirms who is making a request, while authorization determines what they can access. Limit permissions, roles, and scopes to only what an integration requires to reduce the impact of compromised credentials or unauthorized requests.
Protect API Keys and Secrets
Never hard-code API keys, tokens, or credentials into source code or expose them in repositories and client-side applications. Use secure secrets management practices, rotate credentials regularly, and revoke access immediately when keys are compromised or no longer needed.
Secure Data Throughout the Integration
Protect sensitive information as it moves between connected systems by using encrypted connections and appropriate storage controls. Share only the data required for the integration and avoid exposing confidential information through API responses, logs, or error messages.
Validate Requests and Protect Endpoints
Validate incoming data, enforce expected request formats, and reject malformed or unauthorized requests before they reach backend systems. Rate limiting and other API endpoint security controls can also help prevent abuse, brute-force attempts, and resource exhaustion.
Review Third-Party API Security
Third-party APIs can introduce risks beyond a business's direct control. Review their authentication requirements, permissions, data-handling practices, and security responsibilities, especially when API integration in mobile app development connects applications with multiple external services and data sources.
Test the Integration Before Deployment
Security testing should verify authentication, authorization, credential handling, input validation, and endpoint behavior before production. Building secure and scalable applications also requires teams to consider emerging app development trends throughout the development lifecycle.
Insecure vs. Secure API Integration Examples
Seeing these practices side by side makes the difference concrete.
|
Insecure Practice |
Secure Practice |
|---|---|
|
API key hard-coded directly in the application's source code |
API key stored in a secrets manager or environment variable, loaded at runtime |
|
Authorization check only performed in the client-side app |
Authorization check enforced on the server for every request |
|
API response returns the full user object, including internal fields |
API response returns only the fields the integration actually needs |
|
No rate limiting on a public-facing endpoint |
Rate limiting applied per user or API key to prevent abuse |
|
Third-party API response used immediately without validation |
Rate limiting applied per user or API key to prevent abuse |
How Should You Authenticate and Authorize an API Integration?
Secure API authentication and authorization are essential because they determine who can access an API and what they can do once access is granted. Businesses should choose an authentication method that fits the integration's use case and then enforce authorization controls that restrict access to only the required data and functions.
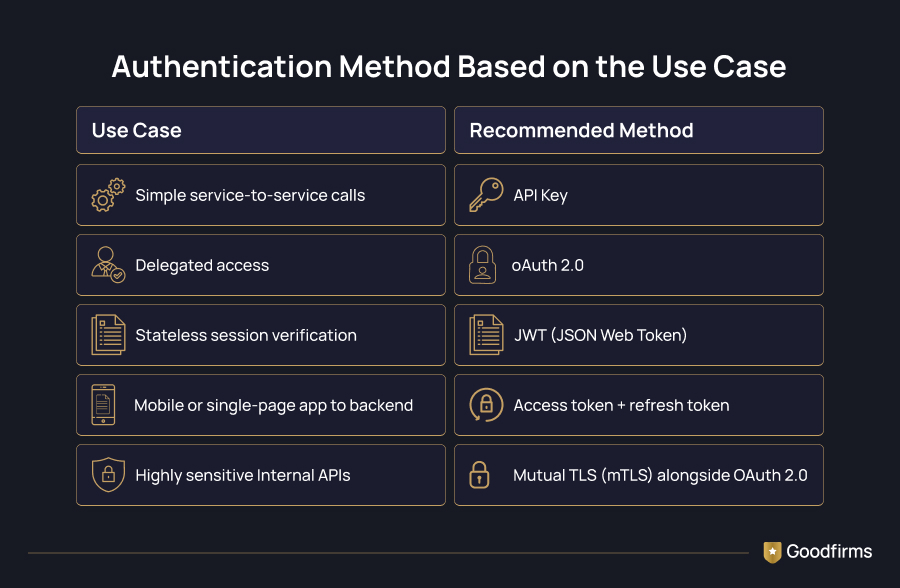
Choose an Authentication Method Based on the Use Case
API keys can work for simpler service-to-service requests, while OAuth 2.0 is better suited to delegated access between applications. Access tokens and other mechanisms should be protected, validated, and configured according to the sensitivity of the API and the data being exchanged.
Treat Authentication and Authorization as Separate Controls
Authentication verifies the identity of a user, application, or service. Authorization determines what that authenticated entity can access. A secure API integration requires both controls, as valid credentials should not automatically grant unrestricted access to every endpoint, function, or data resource.
Apply the Principle of Least Privilege
Grant integrations only the permissions required to perform their intended functions. Restrict overly broad roles and access scopes, and review permissions regularly. This is typically enforced through role-based access control (RBAC), which ties permissions to defined roles rather than individual users or integrations.
This limits the potential damage if an API credential, access token, or connected application is compromised.
Enforce Authorization on the Server Side
Authorization checks should be performed on the server rather than relying on client-side restrictions. This reflects a zero-trust approach to API security — no request is trusted by default, regardless of where it originates. Every request to sensitive data or functionality should be validated to ensure the authenticated user or application has permission to access that specific resource.
Rotate and Revoke Access When Necessary
Access should not remain valid indefinitely. Rotate credentials according to the organization's security policy, revoke compromised tokens immediately, and remove permissions when an integration is retired or no longer requires access. This helps reduce risks associated with forgotten or long-lived credentials.
How Should API Keys and Secrets Be Managed Securely?
API keys, access tokens, passwords, and other secrets should be treated as sensitive credentials because anyone who obtains them may gain access to connected systems or data. Effective API secrets management ensures that these credentials are securely stored, regularly rotated, and immediately revoked when compromised or no longer required.
Never Hard-Code API Keys or Secrets
Hard-coded credentials can be accidentally exposed through source code, repositories, backups, or shared files. Instead of embedding API keys directly into applications, keep them separate from the codebase and use secure configuration or secrets management systems.
Use Secure Secrets Management
Store API credentials in environment variables, dedicated secrets managers, or secure vaults with appropriate access controls. Restrict access to authorized users and applications only, and avoid sharing credentials via email, documents, or unsecured communication channels.
Rotate Credentials Regularly
API key rotation reduces the risk associated with long-lived credentials. Establish a rotation policy based on the integration's sensitivity, and replace keys without disrupting critical services whenever possible.
Revoke Compromised or Unused Credentials
Organizations should be able to immediately disable exposed credentials and remove access for integrations, applications, or users that no longer need it. Regular credential reviews can also help identify forgotten keys and unnecessary permissions.
Monitor Access to Sensitive Credentials
Maintain logs that show when and how sensitive credentials are accessed or used. Monitoring for unusual activity can help teams detect potential misuse early and respond before a compromised API key leads to a larger security incident.
How Do You Protect Data and API Endpoints?
Protecting data and API endpoints requires businesses to secure information throughout its journey and prevent unauthorized or malicious requests from reaching connected systems. Strong encryption, data minimization, input validation, and rate limiting are essential API security best practices for reducing data exposure and endpoint abuse.
Encrypt Data in Transit and at Rest
Use HTTPS and TLS to protect API data in transit between connected applications. Sensitive data stored by an API or related system should also be encrypted at rest to reduce the impact of unauthorized access or a potential breach.
Share Only the Data an Integration Needs
Apply data minimization by limiting the information shared between systems to what is necessary for the intended function. Avoid returning unnecessary fields in API responses, particularly when they contain personal, financial, or other sensitive information.
Validate and Sanitize Incoming Requests
Input validation helps ensure APIs process only expected data and request formats. Validate parameters, enforce schemas, and reject malformed input before it reaches backend systems to reduce the risk of injection attacks and other malicious activity.
Use Rate Limiting to Prevent API Abuse
API rate limiting restricts how frequently users or applications can send requests within a defined period. This is most commonly enforced at the API gateway layer, which sits between client requests and backend services to apply consistent security policies. It can help protect API endpoints from brute-force attempts, automated abuse, and excessive traffic that could affect service availability.
Monitor API Endpoints for Suspicious Activity
Continuous monitoring can help identify unusual request patterns, repeated authentication failures, or unexpected traffic spikes. Logging API activity also enables faster incident investigation and helps teams detect potential security issues with API endpoints before they cause significant damage. Businesses managing multiple APIs can also evaluate API management software to improve visibility and control across their API ecosystem.
What to Do If an API Key Is Compromised
If a key is exposed or suspected of compromise, speed matters more than process. Immediately revoke the compromised key so it can no longer authenticate requests. Issue a new key and update it across every system that depends on it, prioritizing production environments first. Review access logs for the compromised key to identify any unauthorized activity that may have already occurred. Finally, investigate how the exposure happened — a code repository, a log file, a shared document — and close that specific gap so the same key (or the next one) isn't exposed the same way again.
What API Security Risks Should You Check Before Launch?
Before launching an API integration, businesses should check for common API security vulnerabilities that could expose sensitive data, bypass access controls, or create unauthorized entry points. Many of these risks map directly to the OWASP API Security Top 10, the industry-standard framework for the most critical API-specific vulnerabilities. However, a pre-launch review should focus on authorization failures, weak authentication, excessive data exposure, malicious input, unsafe third-party API consumption, and unmanaged endpoints.
Broken Object-Level Authorization
Broken object-level authorization occurs when users or applications can access resources they are not authorized to view or modify. Every request involving a specific object or resource should include server-side authorization checks to verify access permissions.
Broken Authentication
Weak authentication controls can allow attackers to impersonate legitimate users or applications. Before launch, teams should check for poorly protected credentials, weak token validation, insecure authentication flows, and endpoints that allow sensitive actions without proper identity verification.
Excessive Data Exposure
APIs may unintentionally return more information than an application actually needs. Review API responses to ensure sensitive fields, internal data, and unnecessary information are not exposed to users, connected applications, or third-party services.
Injection and Malicious Input
Unvalidated input can allow attackers to send malicious data to backend systems. APIs should validate and sanitize incoming requests, enforce expected formats, and safely reject unexpected or malformed input before it can affect databases or connected services.
Unsafe Consumption of Third-Party APIs
Third-party API responses should not be trusted automatically. Validate the data received from external services, restrict permissions, and prepare for unexpected responses, failures, or security issues that could affect the connected application.
Forgotten or Undocumented API Endpoints
Deprecated, shadow, or undocumented APIs can create security gaps because they may remain accessible without regular monitoring or security updates. This is particularly common in older systems, making accurate API inventories and a broader legacy application modernization strategy essential for identifying and removing unnecessary endpoints.
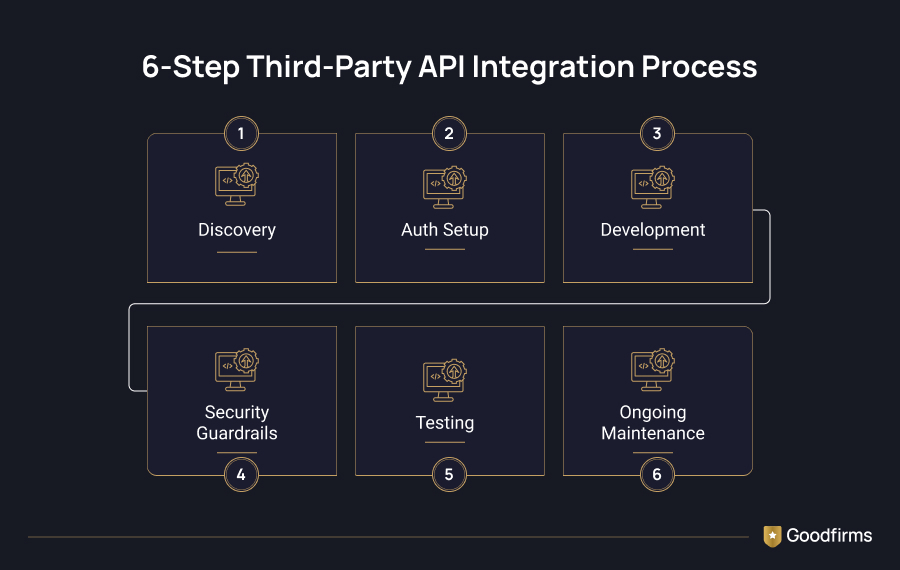
How Should You Assess Third-Party API Security and Test the Integration?
Businesses should assess third-party API security before deployment by reviewing what data an external service can access, how it authenticates requests, and what security responsibilities the provider assumes. The integration should also be tested under realistic conditions to identify vulnerabilities that functional testing alone may miss.
Review the Third-Party API's Access and Security Practices
Check the permissions, access scopes, authentication requirements, and data-handling practices of every external API. Businesses should also understand how providers protect sensitive data, report security incidents, and manage changes that could affect the integration. Checking for compliance with recognized frameworks such as SOC 2, GDPR, or HIPAA can help confirm a provider takes these responsibilities seriously.
Validate Third-Party API Responses
External API responses should not be trusted automatically. Validate incoming data, enforce expected formats, and handle unexpected or malformed responses safely to prevent errors or malicious data from affecting connected applications and backend systems.
Test Security Controls Before Deployment
API security testing should verify authentication, authorization, input validation, credential handling, and rate limits before production. Dedicated API security testing tools can automate much of this verification, particularly for teams managing multiple integrations at once. Forward-deployed engineering also reinforces the importance of accountability for software beyond the development phase.
Prepare for Third-Party Failures
Test how the integration responds when an external API becomes unavailable, slows down, is compromised, or returns unexpected data. Defining fallback behavior and clear failure responses can help prevent a third-party issue from disrupting the entire connected system.
For businesses working with external development partners, these checks should be part of the delivery process rather than an afterthought. Companies evaluating specialized providers, including top blockchain API developers, should ensure that API security testing and third-party risk assessment are clearly defined before launch.
The Complete API Integration Security Checklist Before You Ship
Before deploying an integration, businesses and development teams should verify that essential API security best practices are in place across authentication, data protection, endpoint security, and third-party connections. Use this API security checklist as a final pre-launch review.
Authentication and Authorization
- Every sensitive API endpoint requires appropriate authentication.
- Permissions, roles, and access scopes follow the principle of least privilege.
- Server-side authorization checks prevent unauthorized access to resources.
- Compromised or unused credentials can be revoked quickly.
API Keys and Secrets
- API keys, tokens, and other secrets are not hard-coded or publicly exposed.
- Credentials are stored using secure secrets management practices.
- A process exists for rotating and monitoring sensitive credentials.
Data and Endpoint Protection
- Sensitive data is protected in transit and at rest where required.
- API responses expose only the information necessary for the request.
- Incoming requests are validated, and malformed input is safely rejected.
- Rate limiting and monitoring controls help prevent API abuse.
Third-Party Security and Testing
- External APIs have been reviewed for permissions, data access, and security practices.
- Third-party API responses are validated before being processed.
- Authentication, authorization, and other security controls have been tested.
- The integration has been tested for API failures, unexpected responses, and other realistic scenarios.
A completed API integration checklist should not replace continuous security monitoring, but it provides a practical way to identify critical gaps before the integration reaches production.
FAQs - API Integration Security
What are the best practices for API integration security?
The most important API integration security best practices include using strong authentication, enforcing least-privilege authorization, securing API keys and secrets, encrypting sensitive data, validating requests, applying rate limits, reviewing third-party APIs, and conducting API security testing before deployment.
How should API keys be stored securely?
For effective API key security, keys should never be hard-coded into source code, public repositories, or client-side applications. Instead, store them in environment variables, secure vaults, or dedicated secrets management systems with appropriate access controls, monitoring, rotation, and revocation policies.
What is the safest way to authenticate an API integration?
The safest API authentication method depends on the integration and access requirements. OAuth 2.0 is commonly used for delegated authorization, while securely managed API keys or access tokens may be better suited for specific service-to-service integrations. Regardless of the method, credentials should be protected and regularly reviewed.
How do you secure a third-party API integration?
Third-party API security requires businesses to review authentication requirements, permissions, data access, and provider security practices before deployment. Teams should also validate external API responses, limit unnecessary access, and test how the integration behaves when the third-party service fails or returns unexpected data.
What should be included in an API security checklist before deployment?
An API security checklist should cover authentication, authorization, API key security, secrets management, data encryption, input validation, rate limiting, endpoint monitoring, third-party API risks, and pre-deployment API security testing. Businesses should verify these controls before the integration reaches production.
What is the OWASP API Security Top 10?
The OWASP API Security Top 10 is the industry-standard list of the most critical API-specific security risks, including broken object-level authorization, broken authentication, and unsafe consumption of third-party APIs. Many of the risks covered in this guide's pre-launch checklist directly reflect this framework.
Final Words: Secure API Integrations Before They Become a Risk
A secure API integration is not just about choosing the right authentication method or hiding an API key. Security depends on how every part of the connection works together, from access controls and data handling to third-party dependencies and ongoing monitoring.
The best time to identify a weak permission, exposed credential, or vulnerable endpoint is before the integration reaches production. Fixing those gaps early is usually far simpler than responding to a security incident after real users and business data are involved.
For businesses working with external development partners, security should be part of the delivery process from the beginning. Evaluating experienced top API developers can help businesses build integrations designed to work reliably while ensuring the security controls needed to protect them.